An audit is a systematic, objective, and independent examination of an organisation's reports, processes, or activities to assess their conformity with established criteria. The results are set out as an opinion or as findings, which become the basis for decision-making and improvement.
Although often associated with financial statements, the scope of audit is far wider, from regulatory compliance and operational effectiveness to information system security. In Indonesia, the standards used depend on who performs the audit: the Audit Standards (SA) of IAPI for public accountants, the Global Internal Audit Standards for internal audit, and BPK's examination standards for state finances.
This article covers the meaning of auditing in full: its constituent elements, functions and objectives, types, process stages, the parties who carry it out, and the standards that apply in Indonesia.
What Is the Definition of Audit?
An audit is the systematic process of gathering and evaluating evidence to determine the degree of conformity between actual conditions and established criteria, and then communicating the results to interested parties.
Several definitions from applicable standards and literature:
- The Institute of Internal Auditors (IIA) defines internal audit as an assurance (assurance) and consulting activity that is independent and objective, designed to add value and improve an organisation's operations through a systematic approach to evaluating and improving the effectiveness of risk management, control, and governance (GIAS 2024 Glossary).
- ISO 19011:2018 defines an audit as a systematic, independent, and documented process for obtaining objective evidence and evaluating it objectively to determine the extent to which the audit criteria are fulfilled. Also learn about audit evidence that auditors use.
- Arens, Elder, and Beasley describe an audit as the gathering and evaluation of evidence about information in order to determine and report the degree of conformity between that information and established criteria, carried out by a competent and independent person.
The common thread across all three definitions is the same: an audit is not merely a "check" but an evidence-based process carried out independently against clear criteria.
What Is the Meaning of the Word Audit According to KBBI?
According to the Kamus Besar Bahasa Indonesia (KBBI), the word audit has three meanings. The first two relate to finance: the periodic examination of the financial books of a company or bank, and testing the effectiveness of the flow of money in and out and assessing the fairness of the reports it produces. The third, in computing usage, concerns the examination of equipment, programs, activities, and procedures. In modern practice, the meaning of audit is wider than the dictionary definition because it covers compliance, operations, and information systems, as explained in the section on types of audit below. The word comes from the Latin audire, which means to hear.
Sources: KBBI Online, entry for audit. The difference between audit and accounting is discussed in difference between accounting and auditing.
What Is a Simple Example of an Audit?
As an illustration, a shop records its cash balance in a ledger. An independent examiner counts the cash on hand, then matches it with the records and transaction evidence. Any difference found is recorded as a finding, and the shop owner receives a report with improvement suggestions. The pattern is the same in the audit of a large company: there are criteria (records and policies), there is evidence, there is an independent examiner, and there is a report. For other examples, see operational audit and a compliance audit in the section on types of audit.
What Are the Elements of an Audit?
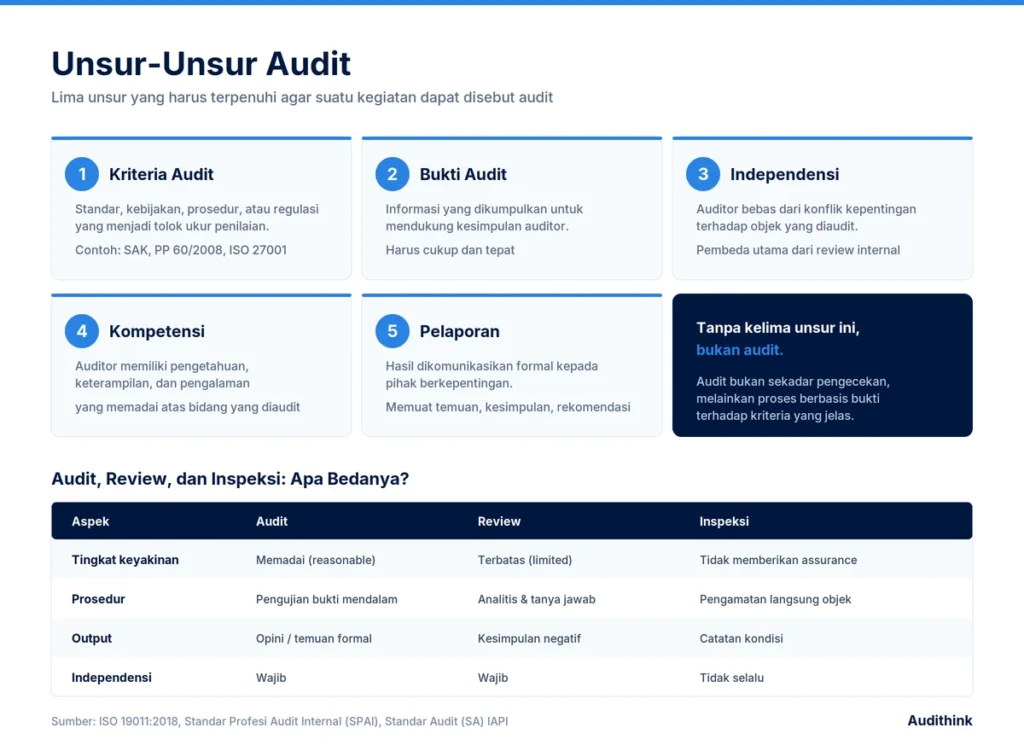
An activity can only be called an audit when it meets the following elements.
1. Audit Criteria
The standards, policies, procedures, or regulations that serve as the benchmark for assessment. Without clear criteria, an auditor has no basis for declaring something fair or unfair. Examples of criteria: SAK for financial statements, Government Regulation 60/2008 for government internal control, or ISO 27001 for information security.
2. Bukti Audit
Information gathered by the auditor to support conclusions; it may take the form of documents, interview results, field observation, third-party confirmation, or system data. Evidence must be sufficient (sufficient) and appropriate (appropriate).
3. Independence and Objectivity
The auditor must be free of any conflict of interest regarding the object being audited. This is what distinguishes an audit from a mere internal review by the people running the process themselves.
4. Auditor Competence
The auditor must have adequate knowledge, skills, and experience in the field being audited.
5. Reporting
Audit results must be communicated formally to interested parties, generally in the form of an audit report setting out the findings, conclusions, and recommendations.
Audit, Review, and Inspection: What Is the Difference?
| Aspect | Audit | Review | Inspection (standalone field examination) |
|---|---|---|---|
| Level of assurance | Reasonable (reasonable assurance), high but not absolute | Limited (limited assurance) | Provides no assurance |
| Procedure | In-depth testing of evidence | Limited to analytical procedures and inquiry | Direct observation of the object |
| Output | Formal opinion/findings | A conclusion with limited assurance | Record of conditions |
| Independency | Mandatory | Mandatory | Not always |
Inspection is also one of the procedures within an audit, namely examining records, documents, or physical assets to obtain audit evidence (SA 500). The Inspection column above compares standalone field examinations, without an assurance conclusion.
What Are the Functions and Objectives of Audit?
An audit is a governance instrument that performs several key functions at once.
1. Ensuring Reliable Information
The most fundamental function of audit is to provide reasonable assurance that the information an organisation presents, whether financial statements, performance reports, or operational data, is reliable. For shareholders, creditors, regulators, and other stakeholders, audited reports become the basis for safer decision-making.
2. Ensuring Regulatory Compliance
An audit tests whether an organisation has carried out its activities in line with laws and regulations, internal policies, and binding contracts. In a financial statement audit, ensuring compliance is management's responsibility; the auditor obtains evidence on provisions that affect the figures and disclosures in the report. For state-owned enterprises, regionally owned enterprises, and government institutions, this function is crucial because it relates directly to accountability for the use of state budgets.
3. Evaluating the Effectiveness of Internal Control
Through control testing, an audit identifies gaps in the internal control system that could give rise to error, inefficiency, or fraud. The auditor's recommendations then form the basis for strengthening those controls.
4. Detecting and Preventing Fraud
Although fraud prevention is management's responsibility, the audit acts as a line of defence that raises the risk of irregularities being detected. The existence of the audit function itself has a preventive effect. A financial statement audit is not designed to find all fraud; for specific suspicions, rely on investigative audit.
5. Providing Recommendations for Improvement
A modern audit does not stop at the findings. Internal auditors provide concrete recommendations for improving process efficiency, optimising the use of resources, and strengthening governance.
6. Enhancing the Organisation's Credibility
A favourable audit opinion is a positive signal to investors, creditors, business partners, and the public. For public sector organisations, an unqualified opinion from the BPK is a widely watched indicator of the quality of financial management.
What Are the Benefits of Audit Results for the Parties Involved?
Audit results are used by several parties, and the benefits differ for each.
| Party | Benefits of audit results |
|---|---|
| Auditee (management and the audited unit) | A picture of control weaknesses and recommendations to improve processes |
| Owners, investors, and creditors | Higher confidence in the financial statements as a basis for decisions (the purpose of an audit under SA 200) |
| Board of Commissioners and Audit Committee | Independent information for oversight; at issuers, internal audit reports are submitted to the president director and the Board of Commissioners (POJK 56/POJK.04/2015 Article 7 letter e) |
| Regulators and government | A basis for assessing compliance and accountability; BPK's audit results on government financial statements contain an opinion and are submitted to the DPR, DPD, or DPRD (Law 15/2004 Articles 16 and 17) |
| Auditors | A basis for expressing an opinion or conclusion with documented evidence |
What Are the Types of Audit?
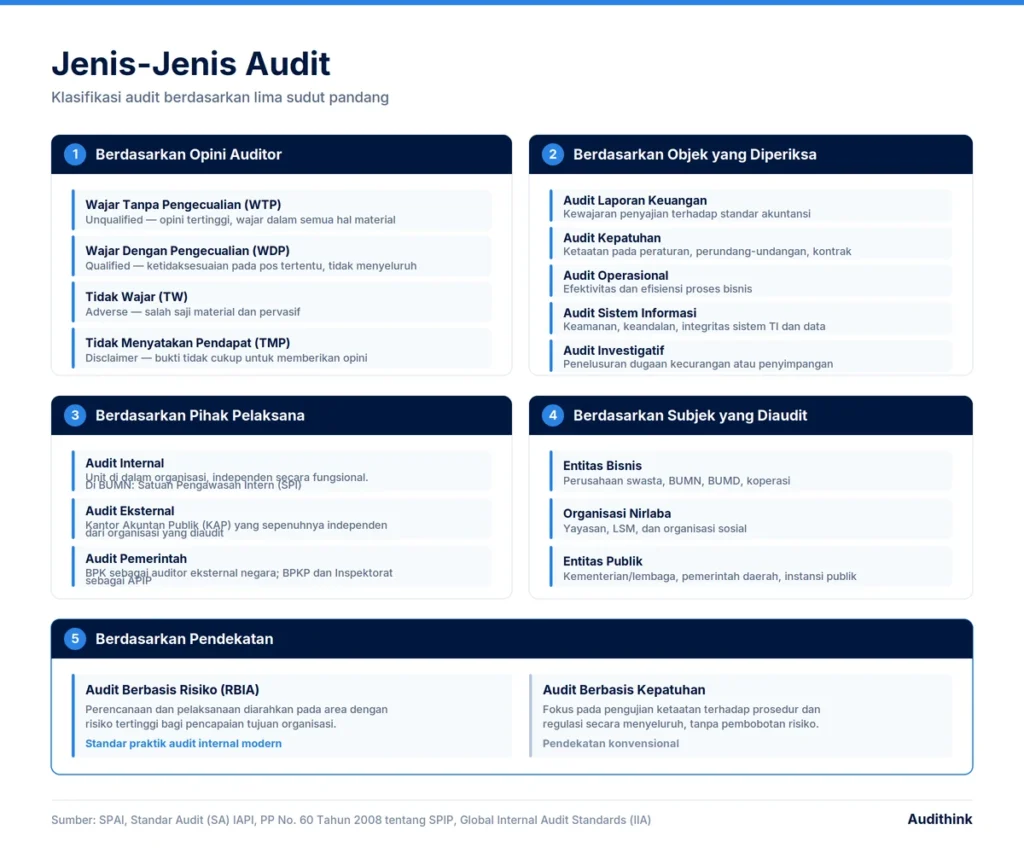
Audits can be classified from several points of view. Understanding these classifications helps an organisation choose the right type of examination for its needs. A fuller discussion is in types of audits.
1. Based on Auditor's Opinion
This classification refers to the final result the auditor expresses on the financial statements.
- Unqualified Opinion (WTP/Unqualified): The highest opinion. The financial statements are presented fairly, in all material respects, in accordance with the applicable accounting standards.
- Qualified Opinion (WDP/Qualified): There are discrepancies in certain items, but they do not affect the statements as a whole.
- Unreasonable (Adverse): There are material and pervasive misstatements, so the financial statements as a whole cannot be relied upon.
- Not Expressing an Opinion (TMP/Disclaimer): The auditor could not obtain sufficient evidence and therefore cannot express an opinion.
2. By the Object Examined
This classification distinguishes audits according to what is being examined.
- Financial Statement Audit: Tests the fairness of the presentation of financial statements against accounting standards.
- Compliance Audit: Tests the organisation's adherence to regulations, legislation, or contracts.
- Operational Audit: Evaluates the effectiveness and efficiency of business processes in achieving the organisation's objectives.
- Information Systems Audit: Assesses the security, reliability, integrity, and availability of the organisation's IT systems and data.
- Investigative Audit: Traces suspected fraud, irregularities, or specific violations.
3. By the Party Carrying It Out
This classification distinguishes audits by the auditor's position relative to the organisation.
- Internal Audit: Carried out by an internal audit unit that is part of the organisation but functionally independent and ideally directly accountable to the board or the most senior leadership (GIAS Standard 7.1). At issuers, the internal audit unit is accountable to the president director and submits reports to the president director and the Board of Commissioners (POJK 56/POJK.04/2015).
- External Audit: Carried out by a Public Accountant who works through a Public Accounting Firm (KAP) and is independent of the organisation being audited.
- Government Audit: Carried out by the Audit Board of Indonesia (BPK) as the state's external auditor, or by the BPKP and the Inspectorate as the Government Internal Supervisory Apparatus (APIP).
4. By the Subject Being Audited
This classification refers to the type of entity that is the auditee.
- Business Entities: Private companies, state-owned enterprises, regionally owned enterprises, cooperatives, and other business bodies.
- Non-Profit Organisations: Foundations, NGOs, and social organisations.
- Public Entities: Ministries and agencies, regional governments, and other public institutions.
5. By Approach
This classification distinguishes audits by the methodology used to determine the focus of the examination.
- Risk-Based Audit (Risk-Based Internal Audit/RBIA): Audit planning and execution are directed at the areas of highest risk to the achievement of the organisation's objectives. GIAS Standard 9.4 requires the internal audit plan to be based on a documented risk assessment performed at least once a year.
- Comprehensive Compliance Approach: Focuses on comprehensively testing adherence to procedures and regulations, without risk weighting.

What Are the Stages of the Audit Process?
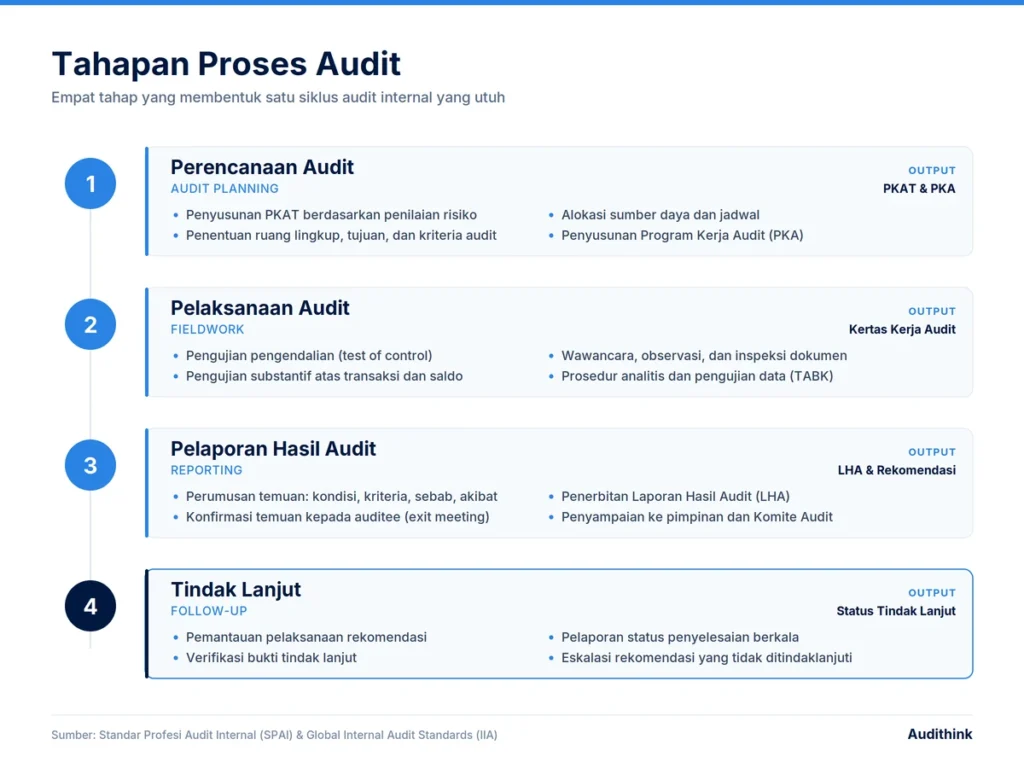
Regardless of type, an audit is carried out through a structured series of stages. The following are the general stages that apply in internal audit practice. A fuller discussion is in the audit process, audit procedure, and audit stages.
1. Audit Planning (Audit Planning)
This stage sets the overall direction of the engagement. Its main activities include:
- Preparing the Annual Audit Work Programme (PKAT) based on risk assessment
- Determining the scope, objectives, and criteria of the audit
- Allocating resources and drawing up the schedule
- Developing an initial understanding of the auditee's business processes
- Preparing the Audit Work Programme (PKA) for the specific engagement
The quality of planning determines the effectiveness of the whole process. Weak planning produces an audit that targets immaterial areas.
See also: The importance of Audit planning and its steps in the examination
2. Conducting the Audit (Fieldwork)
The auditor gathers and tests evidence in the field through:
- Testing of controls (test of control) to assess whether controls are operating effectively
- Substantive testing of transactions and balances
- Interviews with process owners
- Direct observation and inspection of documents
- Analytical procedures and data testing (Computer-Assisted Audit Techniques/TABK)
All procedures and their results are documented in the Audit working paper (KKA) as the supporting basis for the findings.
Procedures for obtaining audit evidence can include inspection, observation, confirmation, recalculation, repeating the work (reperformance), and analytical procedures, and often combine several procedures in addition to inquiries of management (SA 500).
3. Reporting the Audit Results (Reporting)
Findings are formulated and communicated through:
- Drafting findings based on a condition, criteria, cause, effect, recommendation structure
- Confirming the findings with the auditee (exit meeting)
- Issuing the official Audit Report (LHA)
- Submitting the report to leadership and the Audit Committee
The format and content of reports are discussed in audit report.
4. Follow-Up (Follow-Up)
This stage often receives too little attention, even though it determines whether an audit truly adds value. Its activities include:
- Monitoring the auditee's implementation of the recommendations
- Verifying evidence of follow-up
- Reporting the status of recommendation completion at regular intervals
- Escalating recommendations that have not been acted on
An audit whose findings are not followed up produces no improvement at all, only more documents. The causes and solutions are discussed in follow-up on audit findings.
Some organisations manage these four stages with internal audit software so that planning, evidence, and follow-up do not get scattered. A comparison of several options is in 7 Best Internal Audit Management Software for Business in 2026.
What Does an Audit Example Look Like, from Engagement Letter to Follow-Up?
The question “what does an audit actually do” is easiest to answer through a single case. Below is an illustration of an internal audit of petty cash at the Bandung Branch of PT Contoh Niaga. All names, dates, and figures are fictional examples for learning. The branch petty cash fund is set at Rp10,000,000.
| Date (2026) | Stage | What the auditor does |
|---|---|---|
| 2 March | Planning | Engagement letter issued. Objective: assess whether petty cash is managed in accordance with the SOP. Period: February 2026 transactions. Criteria: the petty cash SOP, including approval rules for expenditures above Rp500,000. |
| 3 to 5 March | Planning | Understand the process through an interview with the cashier, then prepare the work program: cash count and sample testing of vouchers. |
| 10 March | Implementation | Surprise cash count, witnessed by the cashier and a branch representative. |
| 11 and 12 March | Implementation | Test 25 vouchers selected from 112 February vouchers, recorded in the working papers. |
| 17 March | Reporting | Exit meeting: the draft findings are confirmed with the branch head. |
| 19 March | Reporting | Audit Report issued. |
| 5 May | Follow-up | The auditor verifies evidence of the fixes. |
What Are the Findings in This Example?
Result of the 10 March cash count: cash on hand of Rp3,150,000 plus unreimbursed vouchers of Rp6,700,000, totaling Rp9,850,000. The fund should be Rp10,000,000, so there is a shortfall of Rp150,000 (1.5 percent of the fund). In the voucher test, 4 of 25 sampled vouchers (16 percent) were above Rp500,000 without written approval, totaling Rp2,480,000.
| Finding elements | Finding 1: cash difference | Finding 2: approval |
|---|---|---|
| Condition | Rp150,000 short at the cash count | 4 of 25 sampled vouchers without written approval |
| Criteria | Cash plus vouchers must equal the fund of Rp10,000,000 | Expenditures above Rp500,000 must be approved in writing by the branch head |
| Cause | Small expenditures paid without vouchers | Approval given only verbally |
| Effect | Money went out without accountability | Expenditures did not go through supervisor oversight |
| Recommendations | Weekly cash count by the branch head | Approval form required before payment |
What Is the Follow-Up?
The branch head committed to completing both recommendations by 30 April at the latest. On 5 May, the auditor checked the evidence: the weekly cash count minutes are available, but the approval form is only partly in use. The first recommendation is closed, while the second remains open and is reported to management. This is how an audit differs from a mere check: there are criteria, evidence, structured findings, and monitoring until completion. The evidence collected is recorded in audit working papers, the results are discussed in audit report, and the follow-up in follow-up on audit findings.
Who Carries Out an Audit?
Who performs an audit varies according to the context and the mandate.
Internal Auditors are part of the organisation and are responsible for providing assurance and consulting to management and the Audit Committee. In state-owned enterprises, this function generally sits with the Internal Supervisory Unit (SPI).
Public Accountants work through Public Accounting Firms (KAP) and are tasked with giving an opinion on financial statements. Public Accountants obtain their licence from the Minister of Finance, their guidance and oversight rest with the Minister, and professional standards (SPAP) must be complied with. The Indonesian Institute of Certified Public Accountants (IAPI) is a professional association and issues the Audit Standards.
Badan Pemeriksa Keuangan (BPK) is the state body authorised to examine the management of, and accountability for, state finances, covering financial, performance, and special-purpose examinations.
The Government Internal Supervisory Apparatus (APIP) consists of the BPKP, the Inspectorates General of ministries and agencies, and Regional Inspectorates. APIP carries out internal oversight of the conduct of government duties.
Information Systems Auditors specialise in assessing IT governance and controls, are generally CISA certified, and use frameworks such as COBIT or ISO 27001.
Who Are the Parties Involved in an Audit?
In general, an audit involves three groups. The auditor examines and delivers an opinion or findings. The auditee is the party being audited, for example management, a work unit, or an agency. The users of audit results are those who use the report to make decisions or exercise oversight, such as owners, creditors, regulators, the Board of Commissioners, and the Audit Committee. SA 200 states that the purpose of a financial statement audit is to increase the confidence of the intended users of the financial statements. For a description of the auditee's role and how a team is organised, read What Is an Auditee and What Is an Audit Team.
What Are the Audit Standards and Regulations in Indonesia?
Audit practice in Indonesia does not operate without rules. The following are the standards and regulations that serve as reference points.
Internal Audit Standards
- Global Internal Audit Standards from the IIA, published in January 2024 and effective on 9 January 2025, serves as the international reference for the internal audit function.
- Internal Audit Professional Standards (SPAI) issued by the Consortium of Internal Audit Professional Organisations, is still known in Indonesia. Check its latest status with the Consortium or IIA Indonesia.
- Internal Auditor Code of Ethics which sets out five principles: integrity, objectivity, competency, due professional care, and confidentiality.
External Audit Standards
- Standard Audit (SA) issued by IAPI and adopting the International Standards on Auditing (ISA), is the mandatory reference for public accountants. More at audit standards.
Public Sector Regulations
- Government Regulation No. 60 of 2008 on the Government Internal Control System (SPIP), which provides the internal control framework for all government institutions, including internal oversight by APIP (Articles 48 and 49).
- State Financial Audit Standards (SPKN) issued by the BPK as the reference for examining state finances.
- Prevailing state-owned enterprise governance provisions, which govern the implementation of good corporate governance (GCG) and the Internal Oversight Unit function at state-owned enterprises. Check the SOE regulator and JDIH for the latest version.
Supporting Standards
- ISO 19011: a guideline for auditing management systems.
- ISO/IEC 27001: an information security management system standard, often used as the criteria for information systems audits.
- COBIT 2019: a framework for enterprise IT governance and management.
Because regulations can change, organisations are advised to refer to the latest version from the official source of each issuing body.
What Are the Challenges in Conducting an Audit?
Clear as the framework is, carrying out an audit in practice often runs into the following obstacles.
Documentation is scattered across many places. Audit working papers are stored in Excel and Word files spread across each auditor's own device, so tracing supporting evidence takes a long time.
Follow-up on recommendations is not monitored. Once the audit report is issued, the completion status of recommendations is often tracked only through a manual spreadsheet that is rarely updated. As a result, the same findings reappear in the following period.
Consolidating findings across units is difficult. For organisations with many units or branches, building a comprehensive risk picture requires manual collation that is prone to error.
Risk-based planning is hard to apply consistently. Without a structured database of risks and historical findings, the annual audit work programme tends to repeat the previous year's pattern rather than follow the current risk profile.
Reporting to the Audit Committee eats up time. Periodic reports are compiled manually from various sources, so auditors spend more time on administration than on analysis.
These obstacles are often structural, not a matter of auditor competence but of working methods that still rely on separate documents. For that reason, some organisations are starting to tidy up how they manage audit plans, working papers, and follow-up with a centralised system.
Frequently Asked Questions
What is meant by an audit?
An audit is a systematic, objective, and independent examination of an organisation's reports, processes, or activities to assess their conformity with established criteria. The result takes the form of an opinion or findings reported to interested parties as a basis for improvement.
What is the main purpose of an audit?
The main purpose of an audit is to provide reasonable assurance about the reliability of information, compliance with regulations, and the effectiveness of internal control. An audit also produces recommendations for improvement that help an organisation manage risk and strengthen governance.
What is the difference between an internal audit and an external audit?
An internal audit is carried out by a unit within the organisation and focuses on evaluating risk management, control, and governance on an ongoing basis. An external audit is carried out by an independent party outside the organisation, generally a public accounting firm, with the main focus of giving an opinion on the fairness of the financial statements for the benefit of third parties.
What are the stages of the audit process?
The audit process generally consists of four stages: planning (determining the scope and a risk-based work programme), execution (gathering and testing evidence in the field), reporting (formulating findings and issuing the audit report), and follow-up (monitoring the implementation of recommendations).
Who is authorised to carry out audits in Indonesia?
It depends on the context. Internal audits are carried out by the internal audit unit or the SPI. Audits of financial statements for public purposes are carried out by Public Accountants through a KAP. Examining state finances is the authority of the BPK, while internal government oversight is carried out by APIP, which covers the BPKP and the Inspectorates.
Which standards govern internal audit in Indonesia?
Internal audit in Indonesia refers to the Global Internal Audit Standards from the IIA and, for some practitioners, the Internal Audit Professional Standards (SPAI). For the government sector, the internal control framework is set out in Government Regulation No. 60 of 2008 on SPIP.
Does auditing only concern financial statements?
No. Financial statements are only one object of audit. Auditing also covers regulatory compliance, operational effectiveness, information system security, and investigation of suspected fraud.
What does audit mean according to KBBI?
KBBI records audit as the periodic examination of the financial books of a company or bank, as well as testing the effectiveness of the flow of money in and out and assessing the fairness of the reports it produces. In computing usage, audit means the examination of equipment, programs, activities, and procedures. In practice, the scope of audit is wider than the dictionary meaning.
Who are the parties involved in an audit?
The parties involved are generally the auditor as the examiner, the auditee as the party being audited, and the users of audit results such as owners, creditors, regulators, the Board of Commissioners, and the Audit Committee. SA 200 states that the purpose of a financial statement audit is to increase the confidence of the intended users of the financial statements.
What are the benefits of audit results for the parties involved?
For the auditee, audit results provide improvement recommendations. For owners, investors, and creditors, an audit increases confidence in the financial statements. For the board and regulators, audit results become the basis for oversight and accountability assessment. For the auditor, audit results are the basis for an opinion supported by evidence.
Read also (types of audit by sector):
- Internal Audit of Community Health Centers: Guidelines, Procedures, and Examples of Implementation
- Clinical Audit: Purpose, Implementation Stages, and Examples
- Sharia Audit: Objectives and Differences from Conventional Audit
- What is an Energy Audit? Learn Its Purpose, Stages, and Examples
- Environmental Audit: objectives, types, examples and stages of implementation
How Can Software Help Manage Audit Plans and Follow-Up?
A well-run audit needs competent auditors and an orderly way of working in planning the audit, preparing the work program, and monitoring the follow-up of findings.
Audithink is customisable internal audit management software tailored to an organisation's needs. Its features include risk assessment, audit planning, work program templates, notifications, follow-up monitoring, and automated reports. Audithink helps manage plans, schedules, and follow-up; the examination itself is still carried out by your auditors.
Discuss your audit team's needs with our team to see how Audithink can be applied to the audit process in your organisation.
Schedule a Demo and see for yourself how Audithink works within your team's workflow; Consultation with Product Expert, and discuss your organisation's specific needs.